
All AI Servers
Scalable AI server platforms for modern workloads
All Multi-node Servers
Maximize compute density for modern data centers.
All General Purpose Servers
Modular enterprise platforms for cloud infrastructure
General Purpose >> EIA Servers
More
All Storage Servers
High-capacity storage for data-intensive workloads
All Motherboards
Form-factor flexibility for system integration
All AMD
AMD platforms for AI and modern data centers
All Intel
Reliable and scalable enterprise server platforms
Rack-scale Solutions
View DetailLiquid Cooling
View DetailDiamond Cooling
View DetailCanonical Ubuntu
View DetailIndustry Applications
View DetailAMD Instinct™ GPU Validated Systems
View DetailMiTAC NVIDIA® Qualified Systems
View Detail
All Resources
Insights & Stories
Media & Catalogs
Technical Documentation
Popular Search
Rack-scale Solutions
View DetailLiquid Cooling
View DetailDiamond Cooling
View DetailCanonical Ubuntu
View DetailIndustry Applications
View DetailAMD Instinct™ GPU Validated Systems
View DetailMiTAC NVIDIA® Qualified Systems
View Detail
- By Category
All AI Servers
Scalable AI server platforms for modern workloads
AI >> OAI Servers
MoreAI >> PCIe GPU Servers
More
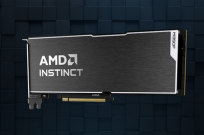
AMD Instinct™ MI350P PCIe® Cards
All Multi-node Servers
Maximize compute density for modern data centers.
Multi-node >> EIA Servers
MoreMulti-node >> OCP Servers
More
All General Purpose Servers
Modular enterprise platforms for cloud infrastructure
General Purpose >> EIA Servers
More
All Storage Servers
High-capacity storage for data-intensive workloads
Storage >> EIA Servers
MoreStorage >> OCP Servers
More
All Motherboards
Form-factor flexibility for system integration
- By CPU Platform
All AMD
AMD platforms for AI and modern data centers
AMD EPYC™ 9006
MoreAMD EPYC™ 9005
MoreAMD EPYC™ 9005/9004
MoreAMD EPYC™ 9004
MoreAMD EPYC™ 8005/8004
MoreAMD EPYC™ 4005/4004
More
AMD EPYC™ 9006
AMD EPYC™ 9005
AMD EPYC™ 8005
AMD EPYC™ 4005
All Intel
Reliable and scalable enterprise server platforms
Intel® Xeon® 6
More5th / 4th Gen Intel® Xeon® Scalable
More
Intel® Xeon® 6
5th Gen Intel® Xeon® Scalable
- News & Events
- News
- Events
- Insights & Stories
- Success Stories
- Technical Insights
- Media Reviews
- Media & Catalogs
- Catalogs
- Technical Documentation
- White Paper
- Data Sheets
- User Guides
Security Center
The latest security information on MiTAC server productsSecurity Center
Security Advisory
AMD SMM Vulnerabilities, Feb. 11 2025 (2025-03-11)
(AMD-SB-7027)
Summary:
Quarkslab reported vulnerabilities that could allow attackers to execute code within SMM (System Management Mode).
CVE-2024-21925 is the result of a lack of sufficient input buffer(s) validation within the AmdPspP2CmboxV2 UEFI module. CVE-2024-0179 is an SMM (System Management Mode) Callout vulnerability within the AmdCpmDisplayFeatureSMM UEFI module. Both can allow ring-0 attackers to escalate their privileges, potentially resulting in arbitrary code execution. AMD has begun releasing firmware mitigations to fix these vulnerabilities.
CVE-2024-21925 is the result of a lack of sufficient input buffer(s) validation within the AmdPspP2CmboxV2 UEFI module. CVE-2024-0179 is an SMM (System Management Mode) Callout vulnerability within the AmdCpmDisplayFeatureSMM UEFI module. Both can allow ring-0 attackers to escalate their privileges, potentially resulting in arbitrary code execution. AMD has begun releasing firmware mitigations to fix these vulnerabilities.
Affected Platforms and BIOS version numbers that contain the fix:
| Product Name (Model Name) | BIOS Version with Fix |
|---|---|
| S8050GM2NE(S8050) | V3.02 |
| S8050GM4NE-2T(S8050) | V3.04 |
| B8050F65TV8E2H-G (FT65TB8050) | V3.02 |
| B8050F65TV8E2H-N (FT65TB8050) | V3.02 |
| B8050F65TV8E2H-2T-N (FT65TB8050) | V3.05 |
| S8016AGM2NR(S8016) | V3.08 |
| B8016H68D5(HG68B8016) | V2.08 |
| B8016G40V4(GX40B8016) | V2.06 |
SUBSCRIBE NOW to get the latest news.
Thank you for your subscription.
Existed email or invalid e-mail!
Successful unsubscription.
Email doesn't exist.